VOLTA Infostealer: How AI Now Ranks What Stolen Data Is Worth
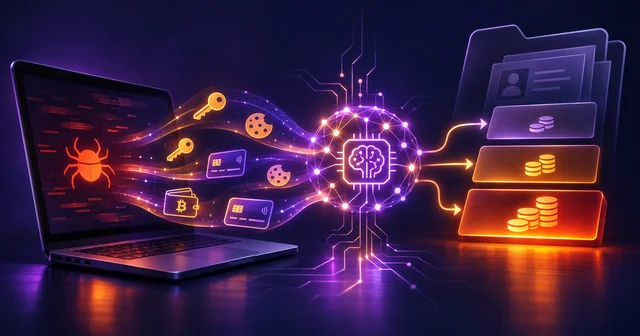
VOLTA is a Windows infostealer, documented by Cisco Talos on October 31, 2026, that sends what it steals to a commercial AI model. The model ranks the victim's money-making assets and builds a dossier on their identity and security habits. The AI is optional, so the theft works without it, and the defences are the usual ones.
What Happened
On October 31, 2026, Cisco Talos researcher Ryan Fetterman published an analysis of VOLTA, which some reports call VOLTA-AUTODOXER. It is a self-deleting Windows infostealer with an optional AI stage. Talos says the sample came to light through CAIRN, the research toolkit it released in September for hunting malware with built-in AI. WIRED reported the story the same day.
The details Talos gives are specific. The analysed binary is a 64-bit Windows executable with a compile timestamp of August 17, 2026, and it was first seen on October 11, 2026. Once it has collected its haul, VOLTA sends a structured evidence bundle to OpenRouter's chat-completions API, a service that routes requests to many AI providers through one interface. By default it asks for Anthropic's Claude Opus 4.6. If the reply contains refusal phrases, VOLTA retries with Moonshot's Kimi K2 and then Google's Gemini 2.5 Flash.
The scale is unclear. According to accounts of WIRED's reporting, Fetterman said Talos had not seen VOLTA used in real attacks and described the sample as a working prototype rather than something circulating widely. Talos names no threat actor, victim count, target region or sector.
Why It Matters
Infostealers are not new. They are one of the most common ways stolen logins end up for sale. What VOLTA changes is the step after the theft. A typical stealer log is a pile of passwords, cookies and session files, and somebody has to sort it. Usually that means a human operator, or a buyer on a criminal market, working out which accounts are worth cashing out first. VOLTA hands that sorting to a language model and gets back a written, ranked report.
Talos frames this as "effort displacement", not speed or scale. The model doesn't steal anything the stealer couldn't already take. It replaces the analyst. That matters because the hard part of making money from stolen data is often judgment: which crypto wallet is funded, which game account holds valuable items, which inbox proves where someone lives. If a low-skill buyer can get that judgment by pasting an API key into a builder, the skill needed to run this kind of operation drops.
Talos also sees VOLTA as part of a pattern. It links it to CLOSEDQUORUM, an earlier implant Talos documented in which AI models decide what the malware does next. In both cases, analysis that used to need a person is now a model call. The refusal-handling chain is the other trend to watch. VOLTA was built expecting at least one AI provider to say no, and it simply moves on to the next one.
How It Works
Talos describes VOLTA as a builder product. The author keeps a template with six swappable slots, including a Telegram channel for delivering results, API keys and settings. Each customer's values are filled in before a binary is compiled for that order. The credentials in those slots are encrypted with a key derived from two constants stored in the same file. Talos notes this gives no real protection, because anyone who reverse-engineers the binary can recover them.
Stage one is ordinary theft, done thoroughly. VOLTA takes passwords, cookies and saved payment cards from Chromium-based browsers, plus Firefox and Thunderbird data. It also takes Outlook profiles, Slack workspaces, Steam and Battle.net sessions, Discord tokens, Telegram sessions and Roblox accounts. It grabs SSH keys and cloud and VPN configurations, Microsoft OAuth tokens and screenshots, and it dumps saved Wi-Fi profiles in plain text. It goes after cryptocurrency wallets with a built-in password cracker. To get past Chrome's newer cookie protection, it uses a path that runs Chrome in headless mode. Google introduced app-bound encryption for Chrome cookies on Windows in 2024, and Talos's top defensive advice targets this headless step.
Stage two is enrichment. VOLTA uses the victim's own Gmail access to search for order receipts from Amazon, DoorDash, Uber Eats, Grubhub, Walmart and PayPal. Those receipts confirm a home address. It pulls food-delivery order history, enriches Discord profiles, and values any Roblox inventory live through the Rolimons trading site. Talos found no attacker-owned servers. Every endpoint it observed belongs to a legitimate third party.
Stage three is the appraisal. VOLTA writes the collected evidence to a file called Identity_Report.txt and sends it to the model at a temperature of 0.2. Talos reads that setting as a preference for consistent, factual output over creative output. The system prompt casts the model as a forensic intelligence analyst writing a target assessment. Required sections include a ranking of the victim's valuables into low, medium and high money-making tiers, and a review of their security habits and password hygiene. The model is asked to link sparse clues, such as a name, an address and patterns across passwords, into a dossier with citations to the evidence. The answer is saved as AI_Analysis.txt.
Stage four is exfiltration. The results leave in stages as ZIP archives: one after collection, one after the AI call, and a third if enrichment found anything. They go to the operator's Telegram. The AI round trip runs from the victim's own computer before anything is sent out. A timestamped log, volta_debug.txt, records what was collected and whether the model call worked. If no API key was supplied, VOLTA skips the AI stage and works as a conventional stealer. So blocking AI services at the network edge would not stop the theft itself.
What's Still Unknown
The biggest open question is whether VOLTA has any real victims. Talos analysed one sample and, as reported, has not seen it in live attacks. Nobody has said who built it, who has bought the builder, or how it reaches victims' machines. Talos's report doesn't name a delivery method such as cracked software, fake installers or phishing attachments.
It is also unclear how good the AI dossiers are. Talos describes the prompt and output format but does not judge whether the model's rankings or identity guesses are accurate. Language models can confidently join unrelated clues, so a dossier could be wrong as easily as it could be useful to a criminal.
Finally, no response from OpenRouter, Anthropic, Moonshot or Google had been reported at the time of writing. Anthropic's usage policy already prohibits malicious cyber activity and tracking or profiling people without their consent. The fallback chain exists because VOLTA's author expected refusals. Whether providers can spot this traffic, and revoke keys fast enough to matter, is untested in public.
Frequently Asked Questions
What is the VOLTA infostealer?
VOLTA, also called VOLTA-AUTODOXER, is Windows malware that steals passwords, cookies, payment cards, chat and gaming sessions, and crypto wallets, then deletes itself. Cisco Talos documented it on October 31, 2026. Its unusual feature is an optional stage that sends the stolen data to a commercial AI model, which writes a ranked report of the victim's most valuable assets and a profile of their identity.
Which AI models does VOLTA use?
According to Talos, VOLTA calls OpenRouter's API and asks for Anthropic's Claude Opus 4.6 by default. If the reply contains refusal phrases, it falls back to Moonshot's Kimi K2 and then Google's Gemini 2.5 Flash. The requests are built by hand as JSON, without an official SDK, and use a low temperature of 0.2 so that the output stays consistent and factual in tone.
Is VOLTA being used in real attacks?
Not as far as anyone has shown. Talos analysed a single sample first seen on October 11, 2026. Accounts of WIRED's reporting quote researcher Ryan Fetterman as saying Talos had not seen it in real attacks and that it looks like a working prototype. Because it is sold as a builder, buyers could still deploy it, so the absence of known victims is not a guarantee.
Does blocking AI services stop VOLTA?
No. The AI stage is optional. If the malware has no API key, or cannot reach the model, it still steals and sends everything as a conventional infostealer would. Blocking OpenRouter or other AI endpoints might deny an attacker the ranked dossier, but your passwords, cookies and wallets would still leave the machine. Defences have to stop the infection and the theft, not just the model call.
How does VOLTA find a victim's home address?
It uses the victim's own signed-in Gmail access to search the inbox for order receipts from Amazon, DoorDash, Uber Eats, Grubhub, Walmart and PayPal. Delivery receipts usually include a street address, so several matching receipts confirm where the person lives. It also pulls food-delivery order history. The AI model is then asked to tie the address to names, accounts and password patterns.
What should I do if I think I was infected?
Talos advises keeping the volta_debug.txt log if you find it, because it lists what was taken and whether the AI call succeeded. From a clean device, revoke sessions and tokens for email, Discord, Slack, Steam and Microsoft accounts, then change passwords. If a wallet seed phrase was stored in plain text, treat the wallet as lost and move funds to a new one created on an offline device.
How can organisations detect VOLTA?
Talos's main recommendation is application control that limits which processes may start Chrome with the headless flag, because VOLTA uses that path to get around Chrome's app-bound cookie encryption. At a minimum, security teams should alert when headless Chrome is launched by an unexpected process. Talos also recommends hardware-backed credential storage and published a file hash and two sample file names as indicators.
Related Reading
Most of what VOLTA takes sits in the browser, so start with our comparison of the best password managers tested in 2026 if your logins still live in Chrome's built-in store. For the endpoint side, our roundup of antivirus software tested and compared covers tools that catch stealers before they run. VOLTA's Gmail receipt search echoes the privacy questions in our explainer on Chrome autofill searching Gmail with Gemini. If a gaming account has already been taken, our guide to recovering and protecting a hacked Roblox account walks through the steps. For another case of abandoned software becoming an attack path, see what Popcorn Time's abandoned updater nearly enabled.